

Future of Business Backup
and Cyber Resilience:
Cyber Resilience, Sovereignty and Rapid Recovery


ISO 27001
Certified
UK Data
Residency
AES 256 Bit
Secure Encryption
Ransomware
Protection
Automated
Hybrid Backup

The Future of
Business Backup:
Cyber Resilience, Sovereignty
and Rapid Recovery
Backup is no longer just about keeping a second copy. UK organisations increasingly need protected recovery points, independent control and evidence that critical data can be restored when the primary environment is compromised.
For years, the future of data backup was described mainly in terms of convenience: more automation, more cloud storage and faster connections. Those changes have arrived. Modern backup software can already protect servers, computers, virtual machines and cloud applications without somebody manually copying files each day.
The more important change is what businesses now expect backup to achieve.
A successful backup is not simply a completed job or a collection of stored files. It is a reliable route back to operation after accidental deletion, hardware failure, account compromise, ransomware or a wider service outage. That changes the questions a business should ask. Where is the recovery copy held? Who can alter or delete it? Can it still be reached if the main administrator account is compromised? How much data could be lost between recovery points? How long would restoration actually take?
The future of business backup is therefore less about storage capacity and more about cyber resilience, recoverability and control.
Backup is becoming part of cyber resilience
Traditional backup planning often concentrated on media failure: a damaged disk, a failed server or a lost laptop. Those risks remain, but recovery planning must now assume that an attacker may deliberately target the backups as well as the live systems.
The UK National Cyber Security Centre’s principles for ransomware-resistant cloud backups make this explicit. The principles address destructive actions, loss of customer access, corrupted later versions, key management and alerts for significant or privileged changes. In other words, the backup environment has to withstand an attack rather than merely store another copy of the affected data.
That is why isolation matters. If production systems and backups depend on the same credentials, administrative accounts or security boundary, one compromise may expose both. A resilient design limits that shared risk through measures such as separate access controls, protected recovery points, restricted deletion and independent storage.
Immutability is one useful control, but it should not be treated as a magic label. Businesses still need to understand what is protected, how long the protection lasts, which administrators retain destructive permissions, and what happens if access to the account itself is lost. The practical objective is straightforward: an attacker who controls the live environment should not be able to remove every viable route to recovery.
Recovery evidence will matter more than backup success reports
Backup dashboards are good at reporting completed jobs. They cannot, by themselves, prove that a business can restore the right data within an acceptable period.
Future backup management will place greater emphasis on recovery assurance. That means testing representative restores, recording the results and correcting failures before an incident occurs. A file-level restore may confirm that individual documents are recoverable, while a server or virtual-machine test can reveal dependencies involving operating systems, applications, credentials and network configuration.
Two measures are particularly useful:
-
Recovery point objective (RPO): how much recent data the organisation can afford to lose, expressed as time.
-
Recovery time objective (RTO): how quickly the service needs to be operational again.
These are business decisions, not merely technical settings. A daily backup may be entirely suitable for one archive but unacceptable for a frequently updated operational database. Likewise, retaining months of history does not guarantee a rapid restore.
The NCSC’s incident planning, response and recovery guidance treats recovery as an organisational responsibility. For an SME, the process does not need to become bureaucratic. A short recovery runbook, named responsibilities, known restore priorities and periodic testing provide far more assurance than an untested assumption that “the data is in the cloud”.
SaaS data needs an independent recovery decision
Business information is increasingly distributed across Microsoft 365, Google Workspace, Box, Dropbox and other hosted applications. These platforms are designed for availability, but service availability is not the same as an independent backup chosen around the customer’s own retention and recovery requirements.
Microsoft’s introduction of Microsoft 365 Backup illustrates how the market has changed. Microsoft now provides a dedicated backup service for Exchange Online, OneDrive and SharePoint, with append-only protection and rapid recovery capabilities inside the Microsoft 365 trust boundary.
That is a significant development, but it does not remove the architectural choice. Some organisations will prefer the speed and integration of a platform-native service. Others will require an independent Microsoft 365 backup held outside the Microsoft platform, particularly where separation of control, supplier independence or UK storage is important.
The correct question is not whether the SaaS provider is reliable. It is whether the recovery arrangement matches the organisation’s risks. A useful assessment should consider:
-
the workloads and data types actually protected;
-
available recovery points and retention periods;
-
whether deleted users and departed employees remain recoverable;
-
the effect of a compromised tenant administrator account;
-
the location and legal jurisdiction of the backup data;
-
export, restore and provider-exit arrangements.
As SaaS estates expand, backup policies will need to follow the data rather than stop at the office network boundary. SaaS backup services and device backup are different technical disciplines, but they should form part of one recovery plan.
Data location and supplier control will remain strategic issues
Cloud services can make infrastructure easier to consume while making the underlying supply chain harder to see. A provider’s business address does not necessarily identify where customer data is stored, which subcontractors are involved, or which jurisdictions apply.
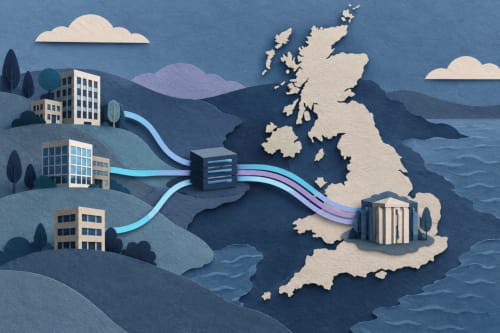
For UK organisations, data residency is becoming a practical procurement question rather than a decorative compliance statement. Legal, care, insurance and public-sector supply chains may require clear answers about storage location, support access and onward processing. Keeping backup data in the UK can simplify those conversations, although location alone does not establish security or regulatory compliance.
The wider issue is control. Businesses should know who operates the service, where the infrastructure sits, how encryption keys and privileged access are managed, and how data can be recovered or removed at the end of the relationship. An independent UK cloud backup provider can offer a clearer separation from the systems being protected, but the service still needs transparent technical and contractual answers.
This scrutiny is likely to increase. The UK Government’s Cyber Security Breaches Survey 2025 to 2026 shows that cyber governance remains uneven across businesses and charities. Backup and recovery should therefore be treated as an accountable business process, not an invisible utility that receives attention only after an incident.
Automation and AI will assist operations, not replace verification
Backup platforms will continue to automate scheduling, retention, monitoring and capacity management. Machine learning can help identify unusual deletion patterns, unexpected data growth, missed protection windows or activity that may indicate ransomware.
Those capabilities are useful because they shorten the time between a problem beginning and somebody noticing it. They do not prove that the stored data is usable.
AI-generated summaries may help an MSP or internal IT team prioritise alerts across many systems. Automated recovery testing may also become more common. Even then, a business should retain human-approved recovery objectives, documented escalation routes and evidence from real restore tests. Automation should reduce repetitive administration while making failures more visible; it should not turn recovery into an opaque decision that nobody has verified.
What a future-ready backup strategy looks like
The technology will continue to change, but the essential questions are already clear. A credible business backup strategy should:
- Identify critical data and services. Include SaaS platforms, servers, PCs, Macs, NAS devices and virtual machines where they support business operations.
- Define recovery priorities. Set realistic RPO and RTO expectations according to the impact of data loss and downtime.
- Separate recovery from production risk. Avoid relying entirely on the same platform, credentials or administrative boundary as the original data.
- Protect recovery points. Use appropriate retention, restricted deletion, version history and ransomware-resistant controls.
- Monitor failures and privileged changes. A silent backup failure is still a failure; significant administrative actions should also be visible.
- Test restores. Confirm that representative data and systems can be recovered, record the time taken and update the recovery runbook.
- Understand data residency and the supply chain. Know where backups are stored, who can access them and what happens when the service ends.
- Review the plan as systems change. New SaaS applications, devices and business processes create new recovery gaps unless protection is updated with them.
The NCSC’s small organisations guide to cyber security places backup alongside account security, device protection and attack awareness. That is the right context: backup is a core resilience control, but it works best as part of a wider security and continuity plan.
The future is recoverable,
not merely backed up
The old ambition was a seamless cloud that copied everything automatically. Automation is now expected. The next stage is more demanding: businesses need recovery copies that remain available when production systems, accounts or suppliers fail.
That makes the future of business backup measurable. Can critical data be restored? From which point? How quickly? Who retains control? Where is the copy held? When was the process last tested?
Organisations that can answer those questions have moved beyond backup as storage. They have built a practical recovery capability.
Deep Blue Backup provides UK cloud backup for SaaS platforms and business devices, with UK-stored options, transparent pricing and direct support. Businesses and MSPs can use the 14-day backup trial to run a real backup and restore test before deciding whether the service meets their recovery requirements.

More backup guidance:
Offsite & Online Data Backup | Data Protection | Backup for Small UK Businesses | Cloud Backup for UK Care Services | Free Data Backup Software

- Dolphin House
Totnes, Devon TQ9 6LX